
Bring what you already have. Mess included.
Onboarding is an upload, not a data-entry project. Nobody types a register in again.
Upload your files
Spreadsheets, CSV exports, PDFs, old audit files.
The agents sort it
They find your assets, people, suppliers and processing activities, fill in owners and classifications, and link them to each other.
Approve and you’re running
The dashboard shows your real readiness on day one.
Evidence lapses. Nobody has to notice.
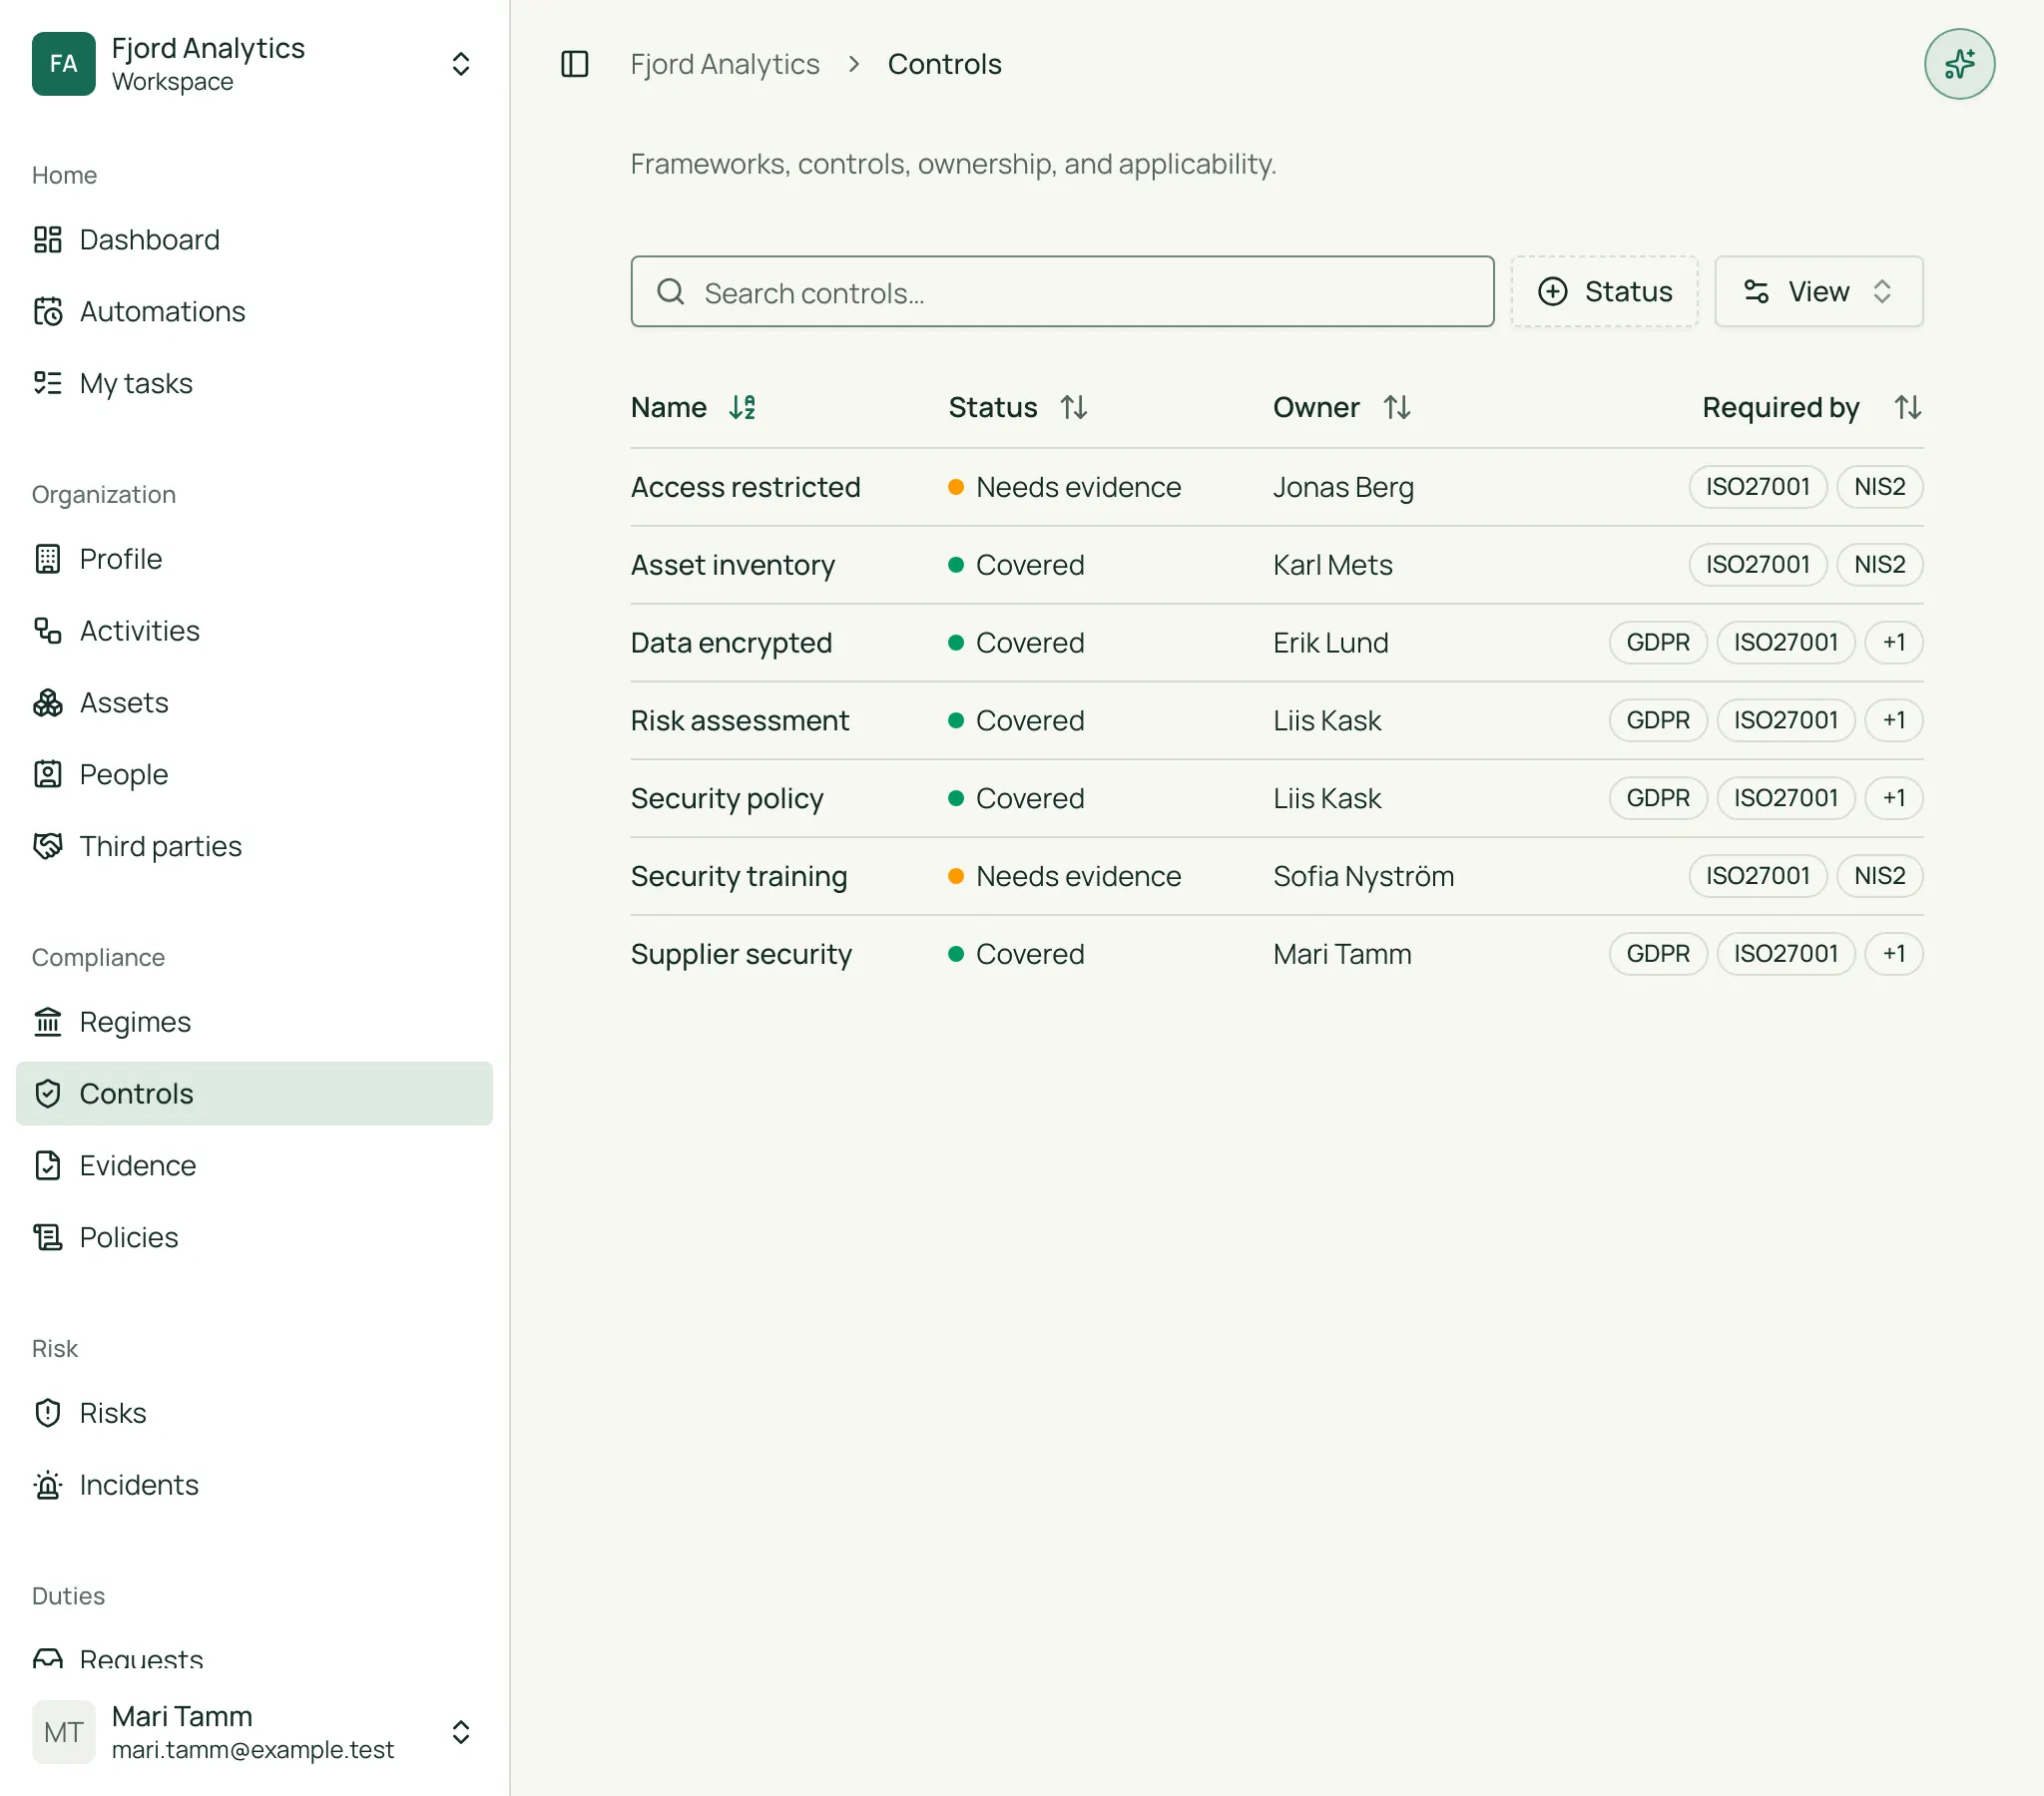
Status comes from the evidence
When evidence passes its renewal date, its control drops back to Needs evidence and an issue opens for the owner.
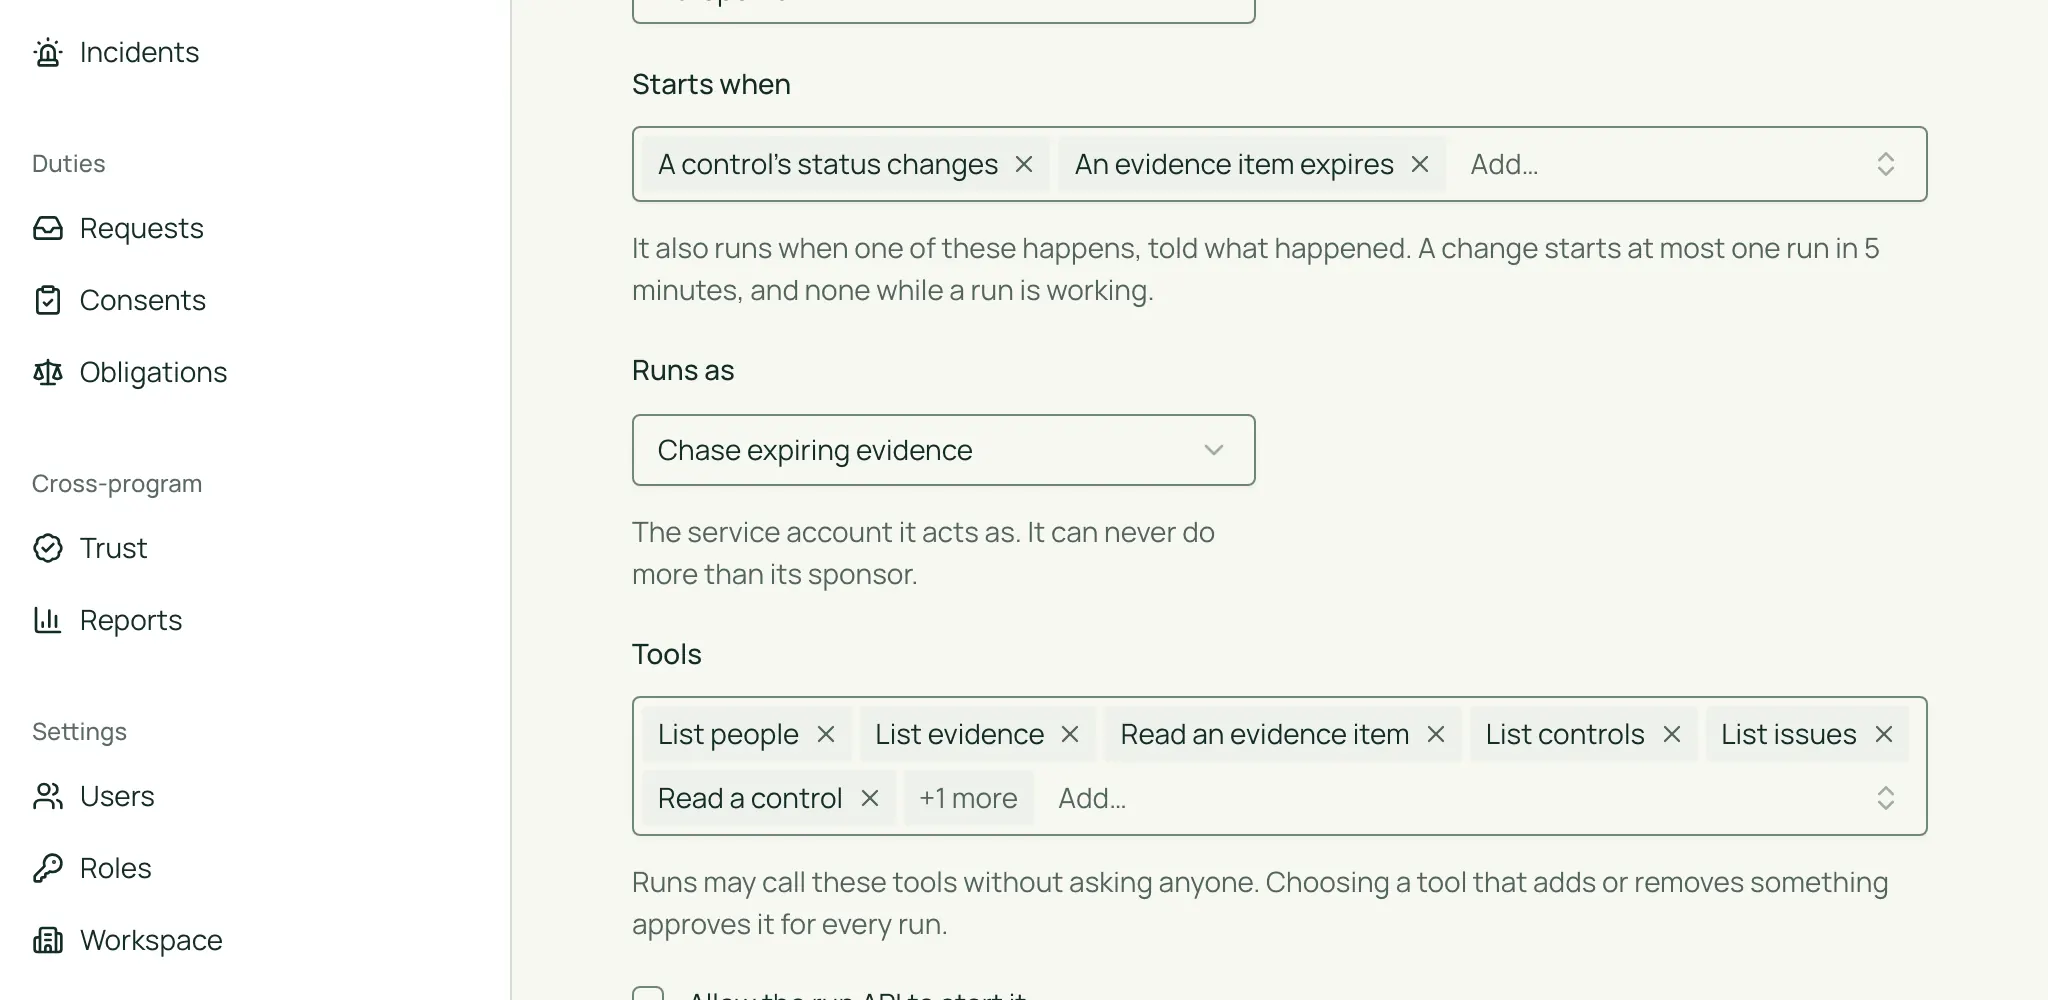
Automations keep watch
An automation runs a prompt on a schedule, or when evidence expires, a control’s status changes or a deadline passes. It writes only with the tools you ticked.
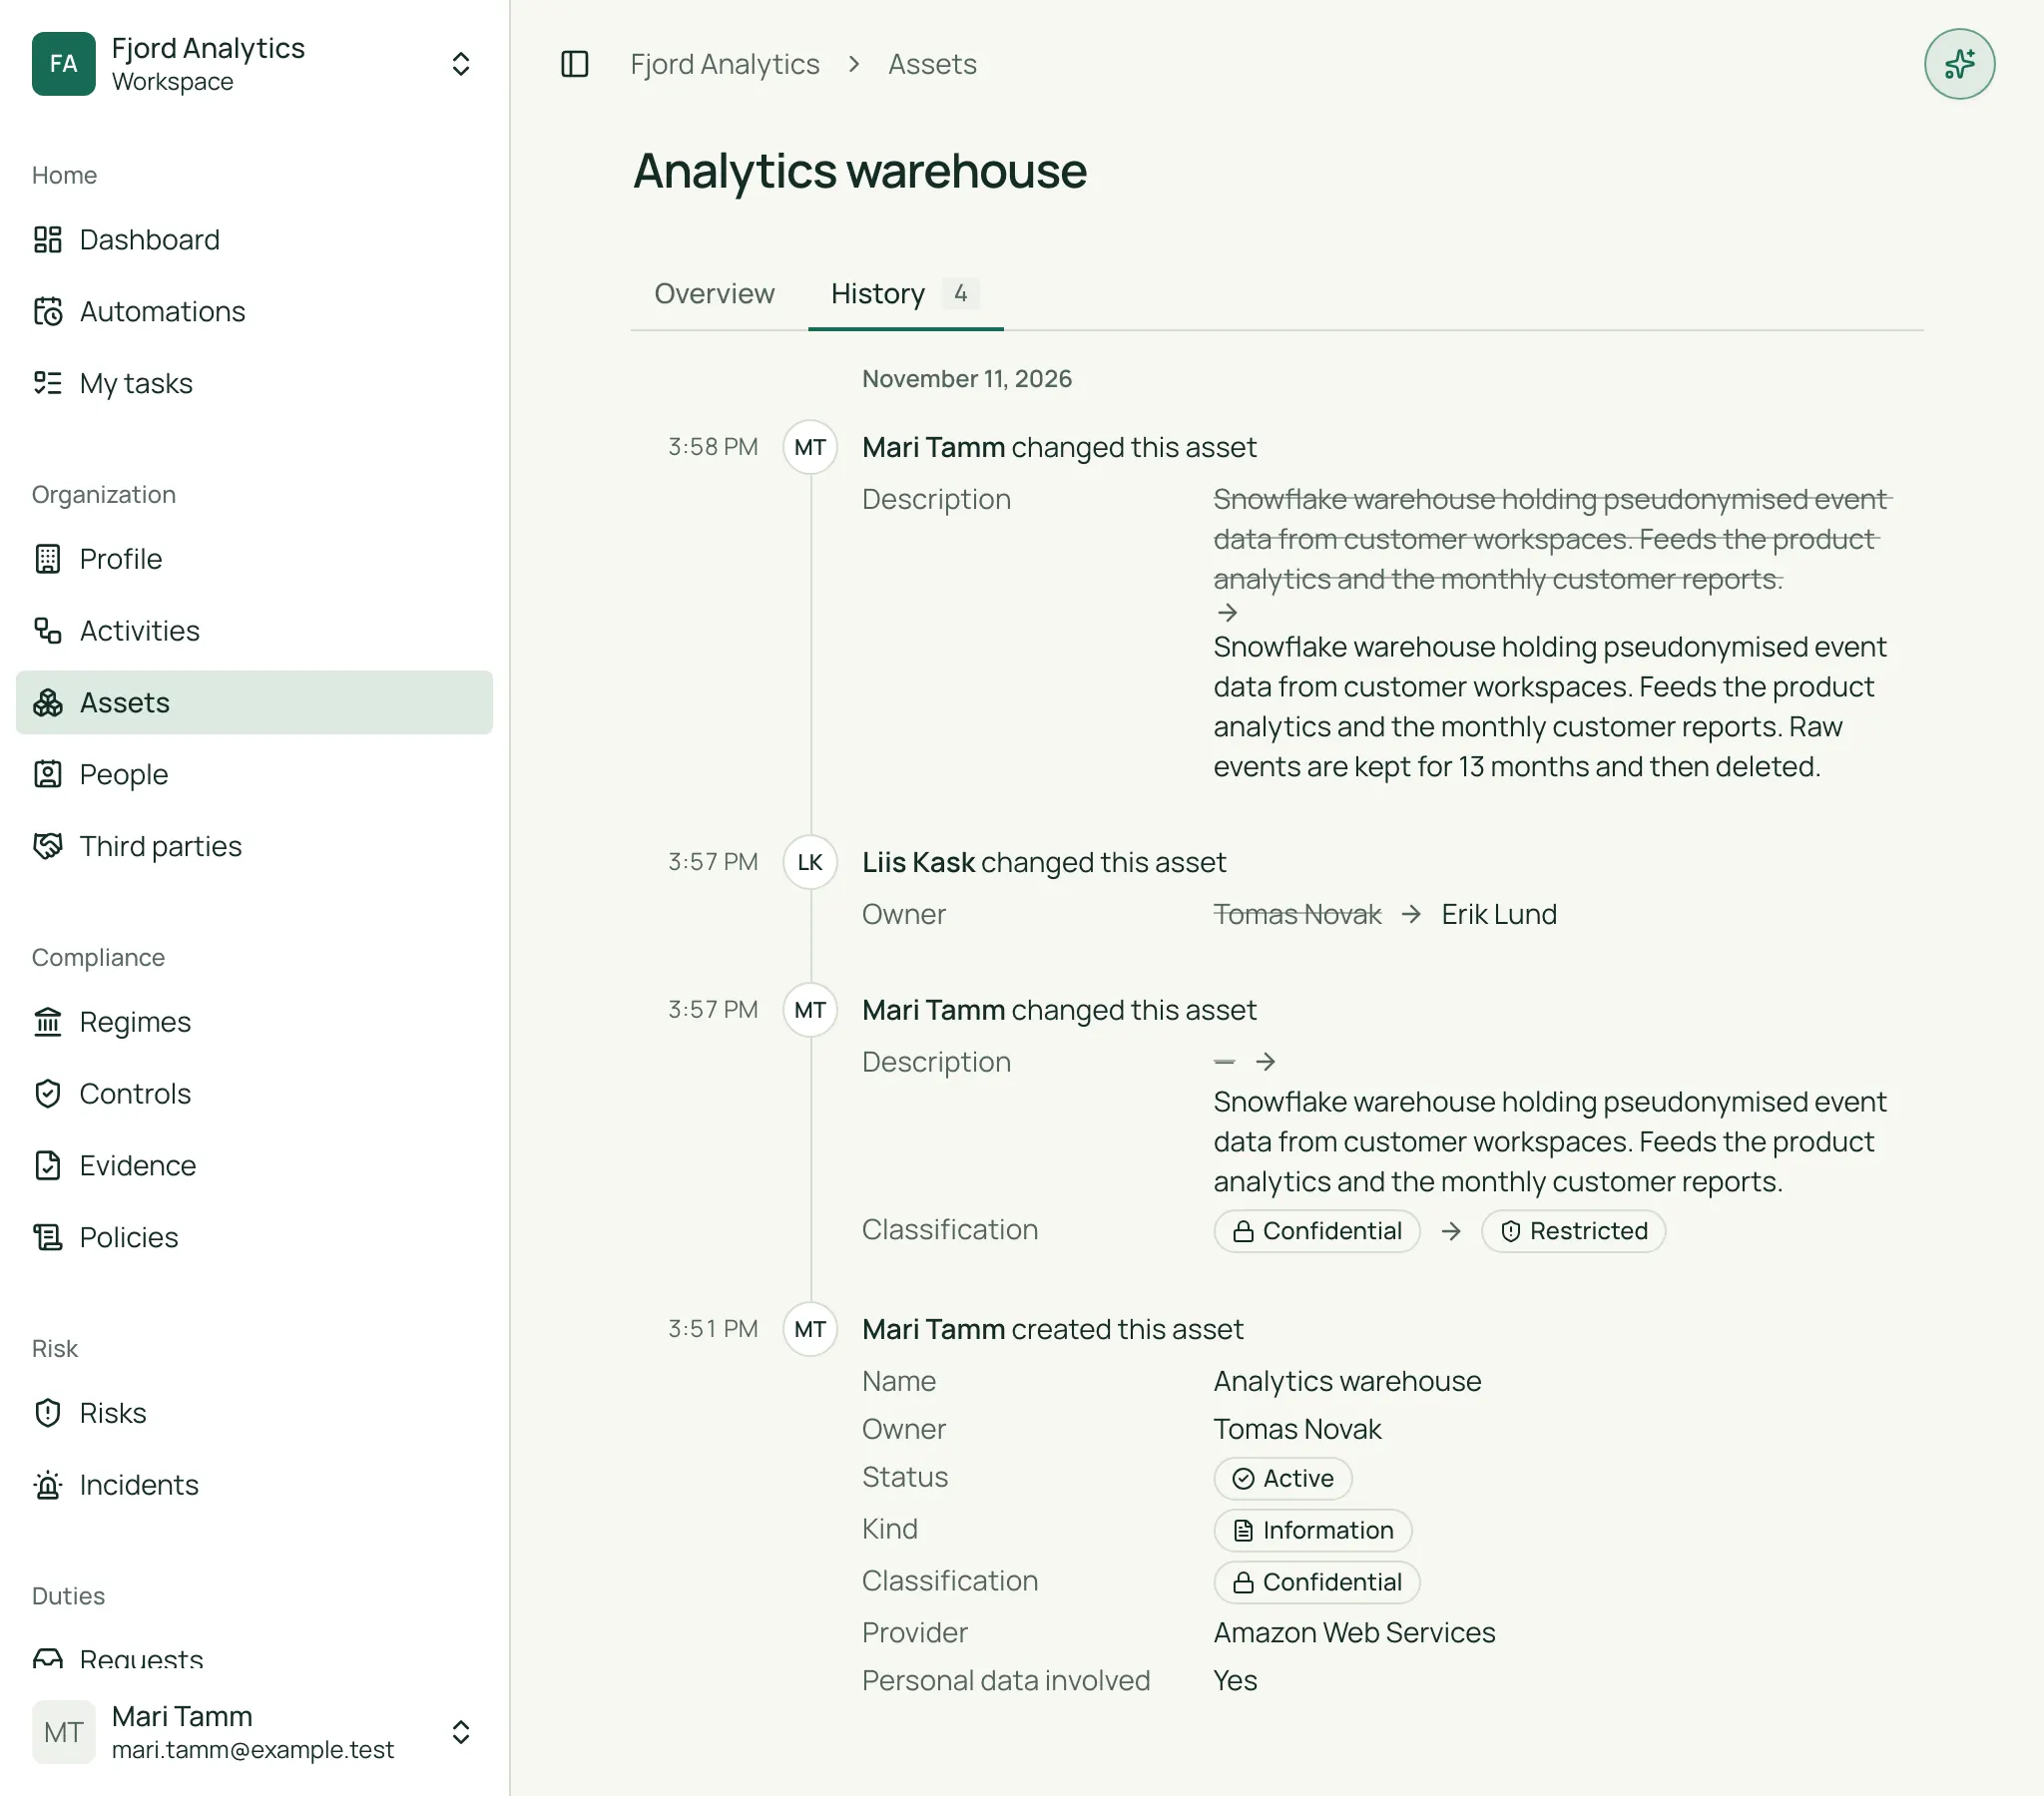
Every change names who made it
A person, a service account or Reguro’s own System account, with the reason for each automatic change.


Ask in Claude. Approve what changes.
Add Reguro to Claude as a connector, or to ChatGPT or any other app that supports MCP, the Model Context Protocol. It works with your permissions.
What’s still missing for ISO 27001?
list_open_workRead, ran without asking
Two controls need evidence: Access restricted and Security training. The new laptops aren’t in your assets yet, so I can add them.
create_assetChange, waiting for you
One control. Every regime that asks for it.
Adopt GDPR now and ISO 27001 next year. A control both require is one control in Reguro, and its evidence counts toward both.
Asset inventory
Asked for by
- NIS2
- DORA
- ISO 27001
- SOC 2
Risk assessment
Asked for by
- GDPR
- NIS2
- DORA
- ISO 27001
- SOC 2
Security training
Asked for by
- NIS2
- DORA
- ISO 27001
- SOC 2
Supplier security
Asked for by
- GDPR
- NIS2
- DORA
- ISO 27001
- SOC 2
Data encrypted
Asked for by
- GDPR
- NIS2
- DORA
- ISO 27001
- SOC 2
Access restricted
Asked for by
- NIS2
- DORA
- ISO 27001
- SOC 2
Security policy
Asked for by
- GDPR
- NIS2
- DORA
- ISO 27001
- SOC 2
| Control | GDPR | NIS2 | DORA | ISO 27001 | SOC 2 |
|---|---|---|---|---|---|
| Asset inventory | Not required | Art. 21(2)(i) | Art. 8(4) | A.5.9 | CC6.1 |
| Risk assessment | Art. 32(2) | Art. 21(2)(a) | Art. 8(2) | 6.1.2 | CC3.2 |
| Security training | Not required | Art. 21(2)(g) | Art. 13(6) | A.6.3 | CC1.4 |
| Supplier security | Art. 28 | Art. 21(2)(d) | Art. 28 | A.5.19 | CC9.2 |
| Data encrypted | Art. 32(1)(a) | Art. 21(2)(h) | Art. 9(2) | A.8.24 | CC6.1 |
| Access restricted | Not required | Art. 21(2)(i) | Art. 9(4)(c) | A.8.3 | CC6.3 |
| Security policy | Art. 24(2) | Art. 21(2)(a) | Art. 9(4)(a) | A.5.1 | CC5.3 |
Pay per seat. Agents don’t take one.
Neither do automations. Every plan includes all five regimes.
Essentials
Keep your records in one place.
€19per seat a month
- Profile, activities, assets and people
- Regimes and policies
- Incidents with their report clocks
Assurance
RecommendedProve your controls with evidence.
€29per seat a month
- Everything in Essentials
- Third parties
- Controls and evidence
- Risks and obligations
Trust
For teams whose customers ask where they stand.
€49per seat a month
- Everything in Assurance
- Trust center (coming soon)
Prices exclude VAT.
Questions.
Do we still need someone responsible for compliance?
One person, not a team. Someone has to own the decisions: approving changes, accepting risks and signing off policies. Agents take on much of the record-keeping and evidence filing.
Does Reguro certify us?
No. Reguro shows how ready you are for each regime and keeps the evidence an auditor asks for. The certificate comes from your auditor.
Where is our data kept?
In the EU, on Google Cloud in Belgium. Each workspace is isolated in the database, and an agent’s access lasts 15 minutes and reaches one workspace only.